Cryptography and Data Security in Pharmaceutical Research: Preparing for the Quantum Era
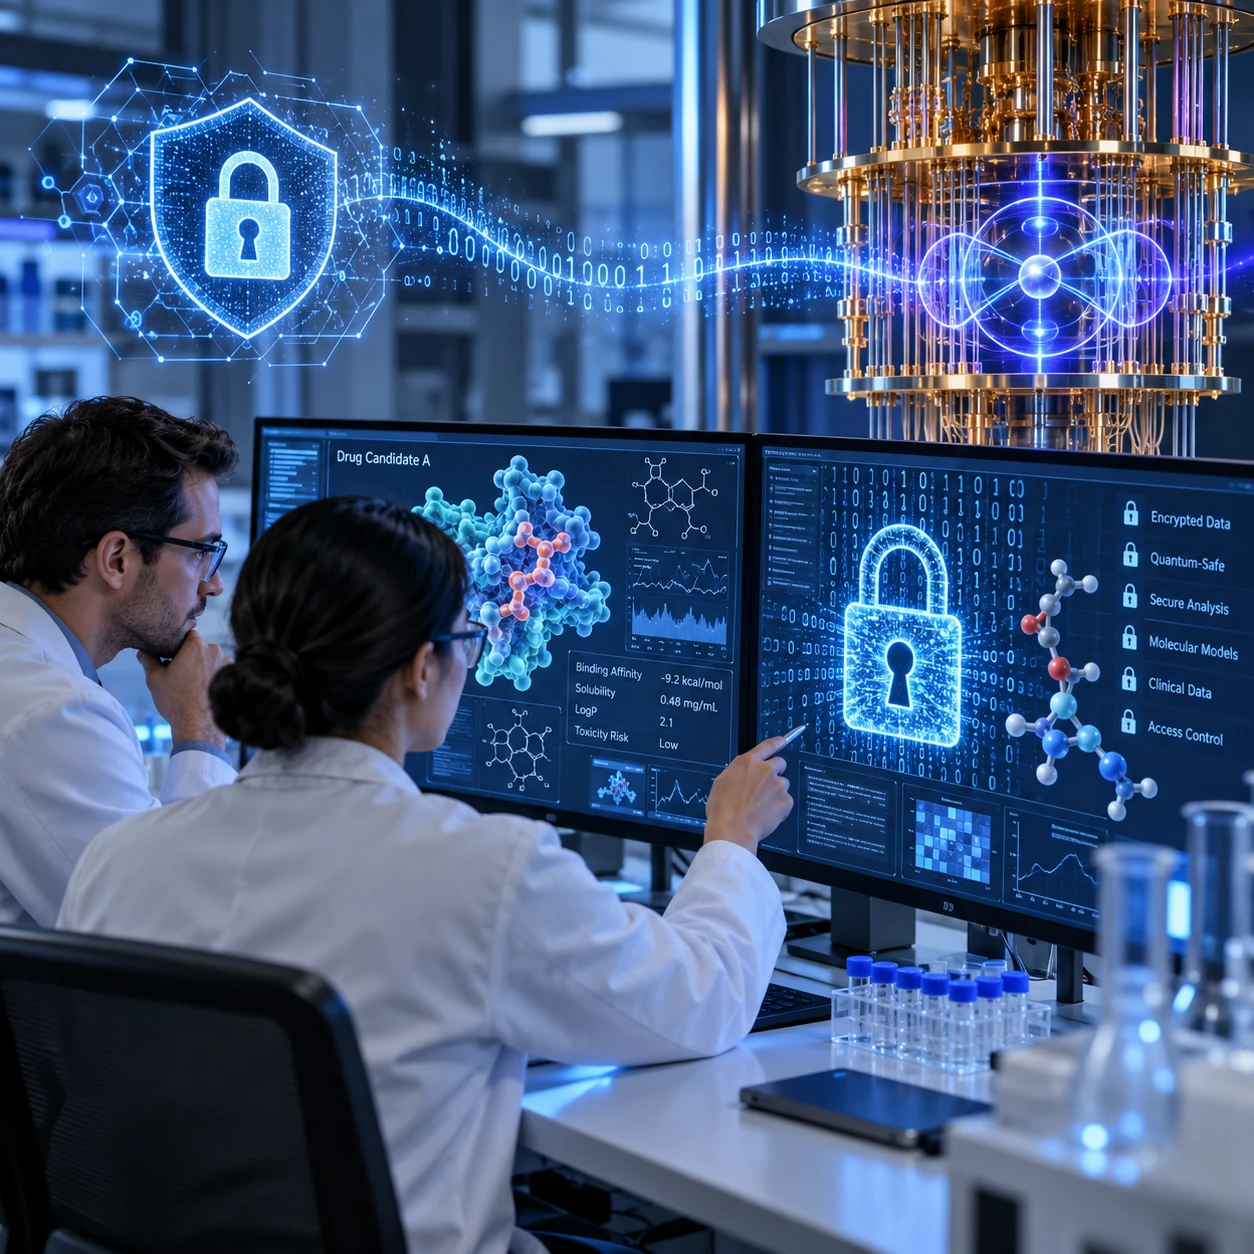
Pharmaceutical research depends on sensitive information: clinical-trial records, genomic data, experimental results, and drug-development plans. Protecting that information requires more than a strong password. Cryptography, access control, and clear collaboration practices help preserve confidentiality, data integrity, and valuable intellectual property across the research lifecycle. Quantum computing adds a future-facing consideration: some cryptographic methods in use today may need to be replaced, so organizations should understand the risk and prepare without treating it as an immediate universal crisis.
Why pharmaceutical research data needs protection
Pharmaceutical research data needs protection because it can identify people, expose confidential findings, and reveal commercially valuable intellectual property. Appropriate safeguards reduce the risk of privacy breaches, research disruption, and loss of control over discoveries.
Different datasets carry different risks. Clinical research may include health records, trial participation details, and adverse-event reports. Genomic information can be especially sensitive because it may reveal inherited traits and, in some cases, link back to an individual or family. Drug-development data can contain candidate structures, assay results, formulation details, manufacturing processes, and unpublished study findings.
The commercial stakes are also significant. A competitor or criminal group that obtains pre-publication results could gain insight into a development program or interfere with a partnership. Intellectual property may be protected through patents, trade secrets, or contractual rights; a security incident can weaken those protections even when no patent application is involved.
Security should match the data rather than rely on a single label. A de-identified dataset may still carry re-identification risk when combined with other information. Teams should assess sensitivity, potential harm, ownership, and retention needs before deciding who can access it and how it should be stored or shared.
Where data-security risks arise across the research lifecycle
Data-security risks can arise at every stage of pharmaceutical research: collection, storage, analysis, transfer, and collaboration. Mapping those stages shows where to apply controls before information moves beyond the original research team.
At collection, risks include misdirected forms, insecure devices, and collecting more personal information than a study needs. During storage, poorly configured cloud services, unpatched systems, or excessive user permissions can expose files. Analysis environments create another challenge: researchers may copy data into notebooks, temporary folders, or third-party tools that do not follow the project’s security rules.
Sharing is often the point where boundaries become unclear. A sponsor, contract research organization, academic lab, sequencing provider, and software vendor may each handle part of a study. An email attachment or public file-sharing link can bypass the controls used in the main research platform.
A practical lifecycle review asks four questions at each handoff:
- What data is moving? Identify personal, genomic, experimental, and commercially sensitive information.
- Who needs it? Limit access to named users and specific project tasks.
- Where will it go? Confirm the destination, storage location, and approved tools.
- How will the team know what happened? Keep access logs and document retention, deletion, and incident procedures.
This map also helps organizations focus effort. A routine transfer of public information does not need the same safeguards as raw genomic data or an unpublished compound-screening dataset.
How cryptography protects research workflows
Cryptography protects research workflows by making data unreadable to unauthorized parties, helping verify who can use it, and supporting checks that reveal unauthorized changes. Its strongest results come when encryption is combined with sound identity, access, and key-management practices.
Encryption at rest protects stored files, databases, backups, and portable devices. If a device or storage medium is lost, encryption can reduce the chance that someone can read the information. Encryption in transit protects data as it moves between a research site, cloud platform, laboratory, or partner system. Both are important: a protected database does not prevent exposure through an unencrypted transfer.
Encryption depends on keys. If keys are stored beside the encrypted data, shared widely, or never rotated when access changes, the protection may fail in practice. Organizations should restrict key access, use managed key-storage systems where appropriate, and define how keys are backed up, rotated, and revoked.
Access control determines which people and services can use specific data. Role-based permissions can give a trial coordinator access to participant records while limiting access to unrelated compound research. Multi-factor authentication, timely removal of former users, and periodic access reviews help keep those permissions aligned with real responsibilities.
Data integrity matters as much as confidentiality. Digital signatures, cryptographic hashes, audit logs, and validated change histories can help a team detect whether a file or record has been altered. These tools do not prove that an experiment was performed correctly, but they can support traceability by showing whether recorded information changed and when.
What quantum computing could mean for today’s cryptography
Quantum computing could eventually weaken some widely used public-key cryptographic methods, but it does not currently make all pharmaceutical data encryption easy to break. The practical concern is long-term exposure: sensitive data captured today could remain valuable after cryptographic capabilities change.
Many systems use public-key cryptography to establish secure connections or exchange keys, alongside symmetric encryption to protect the bulk data. A sufficiently capable, fault-tolerant quantum computer could threaten widely used public-key approaches such as RSA and elliptic-curve cryptography. That possibility is not the same as saying that a current quantum computer can routinely decrypt research archives.
Symmetric encryption is affected differently. Quantum algorithms can reduce the effective security margin of some symmetric-key systems, but they do not provide the same direct break against them as the theoretical threat to certain public-key methods. Security teams should therefore inventory complete systems, not simply label every algorithm “quantum-vulnerable” or “quantum-safe.”
The “harvest now, decrypt later” risk is relevant when information has a long confidentiality lifespan. An attacker could collect encrypted clinical or proprietary data now and retain it in case future advances make decryption feasible. This possibility deserves attention for high-value records, but its likelihood and timing remain uncertain. Current threats, such as credential theft, misconfiguration, and compromised endpoints, still require immediate attention.
Preparing with a post-quantum security strategy
A post-quantum security strategy starts by finding where cryptography is used, prioritizing systems by data sensitivity and lifespan, and planning a controlled migration. Organizations can begin this work now without replacing every security system at once.
Post-quantum cryptography refers to cryptographic algorithms designed to resist attacks from both classical and quantum computers. Standards work is turning these approaches into deployable options, but migration takes time because algorithms are embedded in software, devices, certificates, vendor services, and operational processes.
A practical preparation plan can follow five steps:
- Build a cryptographic inventory. Record algorithms, protocols, certificates, key locations, data flows, and system owners. Include cloud services and research instruments, not only central IT systems.
- Rank data by sensitivity and useful life. Prioritize information that could remain damaging if disclosed years from now, such as identifiable health data or confidential development plans.
- Check dependencies and vendors. Ask providers how they track post-quantum standards, update cryptographic components, and communicate migration timelines.
- Design for change. Favor systems that can replace algorithms without rebuilding the entire platform. Test updates in controlled environments before applying them to active research workflows.
- Coordinate governance and budgets. Assign owners, set review dates, and connect migration decisions to data-retention and procurement plans.
The trade-off is real: adopting new cryptography too early can create compatibility or implementation problems, while waiting until a threat is imminent may leave too little time to update complex systems. A measured, standards-aware transition reduces both risks.
Building security into research collaboration
Secure research collaboration combines technical controls with clear agreements, trained staff, and dependable data-sharing procedures. These measures help partners work with sensitive information while keeping responsibilities and access boundaries visible.
Before sharing data, teams should agree on the purpose, permitted users, approved storage, onward-transfer rules, retention period, and process for reporting an incident. Contracts and data-use agreements can clarify responsibilities, but they do not replace technical safeguards or day-to-day oversight.
Use an approved collaboration environment with named accounts, encryption in transit and at rest, access logs, and permissions limited to the project. Avoid sending sensitive files through personal email or creating unrestricted links for convenience. For recurring transfers, automate secure delivery where possible and verify recipients through a separate channel when instructions change unexpectedly.
Staff practices matter too. Train researchers to recognize phishing, report misdirected data quickly, protect devices, and question unusual requests for credentials or files. Give each partner only the access required for its role, then review that access when a study phase ends or a person leaves the project.
Good governance makes these safeguards usable. A security process that blocks legitimate analysis may encourage workarounds, so involve researchers when choosing tools and define a clear route for requesting access. The goal is controlled collaboration that supports the research, with a visible record of who accessed which data and under what conditions.
Frequently asked questions
Could quantum computers break pharmaceutical data encryption today?
No currently demonstrated, general-purpose quantum computer can routinely break the encryption protecting pharmaceutical research data. The long-term concern is that future quantum systems may threaten some public-key methods, which is why organizations should inventory their cryptography while continuing to address present-day risks.
What is post-quantum cryptography?
Post-quantum cryptography uses algorithms designed to remain secure against attacks from classical and quantum computers. It is intended for deployment on conventional systems, unlike quantum cryptography, which relies on quantum technologies.
Which pharmaceutical research data should be prioritized for protection?
Prioritize data according to sensitivity, potential harm, and confidentiality lifespan. Common priorities include identifiable clinical and genomic information, unpublished drug-development results, proprietary methods, and records covered by contractual or privacy obligations.
How can research partners share sensitive data securely?
Use an approved platform with encryption, named accounts, least-privilege access, and audit logs. Agree in advance on permitted use, retention, onward sharing, and incident reporting, then revoke access when a partner no longer needs it.